Hackers Heat French Supermarket Fridges to 50 Degrees
Set Trending Topics as a preferred source on Google.
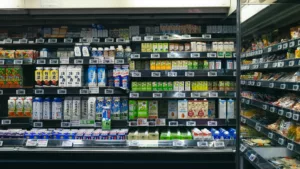
Hackers in France turned up the heat on supermarket shelves: Overnight into Monday, unknown attackers remotely manipulated the refrigeration systems of hundreds of supermarkets. Freezers and refrigerated shelves warmed up, and many stores now have to throw out all their fresh and frozen products. At Intermarché alone, around 150 stores are reported to be affected.
Hundreds of Stores Affected
According to French media reports, the attack began around midnight in some stores. The attackers are said to have forced the refrigeration systems into a permanent defrost mode, driving temperatures as high as 50 degrees Celsius. When staff opened the refrigerators, “a heat wave escaped,” an industry source told the broadcaster BFMTV. What is known so far:
- Intermarché: 150 to 200 stores are affected, according to the news agency AFP.
- Coopérative U: The chain, which runs Super U and Marché U, confirmed disruptions at fewer than 100 outlets.
- Other chains: Media reports also name Leclerc, Carrefour Market and Monoprix, but those chains have not yet confirmed this.
Dominique Schelcher, the head of Coopérative U, wrote on X that the cyberattack was “extremely serious and unprecedented” and called it “unacceptable.” The Paris prosecutor’s office has opened an investigation, covering among other things the food losses and several fires. Who is behind the attack is unclear. Individual stores are said to face losses of several hundred thousand euros, and Intermarché expects that insurance will not cover such damage.
Why Fridges Can Be Hacked
Refrigeration in modern supermarkets has long been networked. Central controllers, known as system managers, regulate temperatures, defrost cycles and alarms for every refrigerated shelf and freezer in a store. To let refrigeration technicians service the equipment remotely, these controllers are often reachable over the network. Anyone with access to such a controller can change set points and trigger defrost cycles.
In this case, the targeted controllers were made by the Danish manufacturer Danfoss, which equips many French supermarkets. According to French media, only older versions of the control software are affected. That such devices are vulnerable has been known for months: Over the summer, the security company Claroty published three vulnerabilities in the web interface of Danfoss’s AK-SM 800A system manager. One of them sits in a hidden “code of the day” mechanism that can be used to bypass authentication and run arbitrary code. Danfoss fixed the flaws with firmware version R4.3.1. Claroty found similar vulnerabilities in a competing product, Copeland’s XWEB Pro.
Whether the attackers exploited these exact flaws has not been confirmed. Danfoss has not yet commented publicly, and a meeting with refrigeration service companies was planned for Monday. The underlying problem is well known in the industry: Controllers in refrigeration systems, buildings and factories often run outdated software for years, because updates interfere with ongoing operations.
Ahold Delhaize Also Reports Problems
At almost the same time, the Dutch-Belgian retail group Ahold Delhaize confirmed a security incident in its network. Websites and apps at Albert Heijn and Delhaize are offline, and several distribution centers have stopped operating. So far, there is no indication of a link to the attacks in France.